
使用Openssl 自签发IP证书
日常交付项目中,总是有这样的场景,再使用一些融合通讯的业务时,需要HTTPS 环境,那就涉及到SSL 证书的签发
考虑到项目成本的问题,往往都是本地自签发IP 证书使用;使用openssl生成根证书,签发服务端证书,安装根证书使浏览器信任自签证书。
- 环境: centos7.9
- IP: 172.16.10.110 111.111.111.111
创建证书脚本:ssl.sh
[root@all ~]# mkdir ssl
[root@all ~]# cd ssl
[root@all ssl]# vim ssl.sh
证书脚本内容:
#!/bin/sh

# Generate the openssl configuration files.
echo "创建openssl.cnf------------------->"

cat > openssl.cnf << EOF
[req]
distinguished_name = req_distinguished_name
req_extensions = v3_req
[req_distinguished_name]
countryName = Country Name (2 letter code)
countryName_default = CN
stateOrProvinceName = State or Province Name (full name)
stateOrProvinceName_default = HN
localityName = Locality Name (eg, city)
localityName_default = ZZ
organizationalUnitName  = Organizational Unit Name (eg, section)
organizationalUnitName_default  = tx
commonName = commonName
commonName_default = tx
commonName_max  = 64
[ v3_req ]
# Extensions to add to a certificate request
basicConstraints = CA:TRUE
keyUsage = nonRepudiation, digitalSignature, keyEncipherment
subjectAltName = @alt_names
[alt_names]
IP.1 = 172.16.10.110
IP.2 = 111.111.111.111
EOF

echo "创建v3.ext------------------->"
cat > v3.ext << EOF
authorityKeyIdentifier=keyid,issuer
basicConstraints=CA:FALSE
keyUsage=digitalSignature, nonRepudiation, keyEncipherment, dataEncipherment
subjectAltName=@alt_names
[alt_names]
IP.1 = 172.16.10.110
IP.2 = 111.111.111.111
EOF

echo "创建CA 根证书------------------------->"
echo "创建私钥 ca.key"
openssl genrsa -out ca.key 2048

echo "创建CA证书 ca.crt"
openssl req -new -x509 -days 3650 -key ca.key -out ca.crt

echo "生成服务器证书----------------->"
echo "创建私钥 server.key"
openssl genrsa -out server.key 2048

echo "创建服务器证书请求文件 server.csr"
openssl req -new -days 3650 -key server.key -out server.csr -config openssl.cnf

echo "创建服务器证书 server.crt"
openssl x509 -days 3650 -req -sha256 -extfile v3.ext -CA ca.crt -CAkey ca.key -CAcreateserial -in server.csr -out server.crt

echo "创建pem------------------------>"
cat server.crt server.key > server.pem

echo "创建p12----------------------->"
openssl pkcs12 -export -in server.crt -inkey server.key -out server.p12 -name "server"
签发证书
#!/bin/sh

# Generate the openssl configuration files.
echo "创建openssl.cnf------------------->"

cat > openssl.cnf << EOF
[req]
distinguished_name = req_distinguished_name
req_extensions = v3_req
[req_distinguished_name]
countryName = Country Name (2 letter code)
countryName_default = CN
stateOrProvinceName = State or Province Name (full name)
stateOrProvinceName_default = HN
localityName = Locality Name (eg, city)
localityName_default = ZZ
organizationalUnitName  = Organizational Unit Name (eg, section)
organizationalUnitName_default  = tx
commonName = commonName
commonName_default = tx
commonName_max  = 64
[ v3_req ]
# Extensions to add to a certificate request
basicConstraints = CA:TRUE
keyUsage = nonRepudiation, digitalSignature, keyEncipherment
subjectAltName = @alt_names
[alt_names]
IP.1 = 172.16.10.110
IP.2 = 111.111.111.111
EOF

echo "创建v3.ext------------------->"
cat > v3.ext << EOF
authorityKeyIdentifier=keyid,issuer
basicConstraints=CA:FALSE
keyUsage=digitalSignature, nonRepudiation, keyEncipherment, dataEncipherment
subjectAltName=@alt_names
[alt_names]
IP.1 = 172.16.10.110
IP.2 = 111.111.111.111
EOF

echo "创建CA 根证书------------------------->"
echo "创建私钥 ca.key"
openssl genrsa -out ca.key 2048

echo "创建CA证书 ca.crt"
openssl req -new -x509 -days 3650 -key ca.key -out ca.crt

echo "生成服务器证书----------------->"
echo "创建私钥 server.key"
openssl genrsa -out server.key 2048

echo "创建服务器证书请求文件 server.csr"
openssl req -new -days 3650 -key server.key -out server.csr -config openssl.cnf

echo "创建服务器证书 server.crt"
openssl x509 -days 3650 -req -sha256 -extfile v3.ext -CA ca.crt -CAkey ca.key -CAcreateserial -in server.csr -out server.crt

echo "创建pem------------------------>"
cat server.crt server.key > server.pem

echo "创建p12----------------------->"
openssl pkcs12 -export -in server.crt -inkey server.key -out server.p12 -name "server"
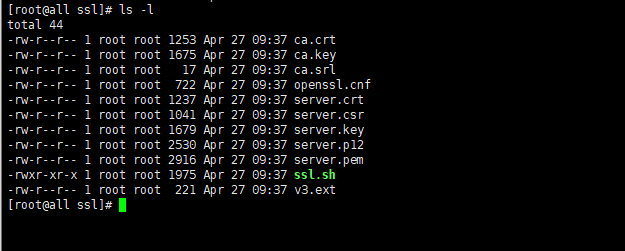
签发好的证书
安装根证书使浏览器信任自签证书。
把刚刚生成的server.crt 导入到本地
导入帮助手册: https://jingyan.baidu.com/article/ca41422fda393f5faf99ed0d.html
文章来源:https://www.cnaaa.net,转载请注明出处:https://www.cnaaa.net/archives/8242